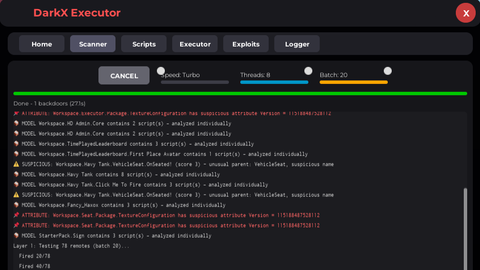
DarkX ServerSide Executor
Universal Script 📌Uploaded by
Description
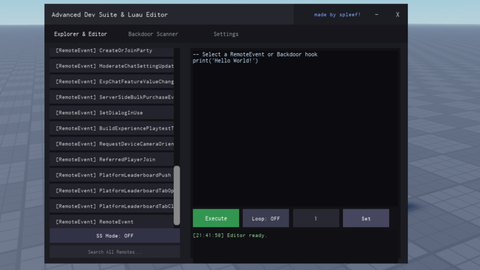
So I’ve been working on this for a while – a tool that actually finds hidden backdoors in games, not just the obvious ones. It’s called DarkX Executor, and it’s built around a multi‑layer scanner that digs deep into every corner of a game to uncover even the most obfuscated server‑side backdoors. What makes the scanner different? Most scanners just look for remote events or basic require calls and call it a day. DarkX does a lot more. It runs through multiple detection layers: Layer 1 – Remote Testing It fires test payloads at every remote event/function it can find. If a remote creates a part in the workspace, it’s flagged as a backdoor. Layer 2 – Signature Patterns It scans scripts for telltale signs like loadstring, require with asset IDs, game:HttpGet, hookfunction, hookmetamethod, getrawmetatable, even obfuscation stuff like bit32.bxor or string.char. If it sees any of these, it raises a flag. Layer 3 – HTTP Backdoors It checks for any script making HTTP calls (HttpGet, HttpService:GetAsync, PostAsync, RequestInternal). Then it actually follows the link – if that link returns an asset ID, it traces it down. That’s how you catch those two‑stage payloads. Layer 4 – Obfuscation Detection It calculates entropy to spot high‑entropy strings (encrypted or packed code) and detects bytecode (scripts that aren’t plain text). Also watches for anti‑debug tricks like checking JobId or IsStudio. Layer 5 – Model Analysis It doesn’t just check scripts – it dives into every model, looks for scripts hidden inside parts, tools, accessories, welds, whatever. If a model contains scripts, it scans each one individually. Layer 6 – Attribute Scanning Some backdoors store asset IDs or commands in instance attributes. DarkX reads every object’s attributes and flags anything suspicious. Layer 7 – Unusual Parent Check If a script is sitting in a weird place – like a blacklisted service (LogService, Stats, etc.) or inside a part where it has no business – it gets flagged. Anything that scores high enough gets tagged as a backdoor and added to the list you can execute on. It even finds suspicious StringValue objects that contain Lua code. Beyond scanning Once you’ve found the backdoors, you can: Execute your own Lua through them (with an optional anti‑logger that replaces your script with “DarkX PWNED YOU” so skids’ loggers see nothing). Use the Exploits tab to target other players with replication‑based attacks – crash, freeze, kill, ragdoll, remove limbs, memory exhaust, blocklist crash, client injection, you name it. Hit the HIJACK GAME button – this deletes every backdoor it found, injects a permanent backdoor Exser into the game, and sets up monitors to destroy any new backdoors that appear. Your backdoor stays in control for the whole server session, and only you can use it. There’s also a Logger tab that hooks remote calls in real time so you can see what other exploiters are trying to run. Why I built it I got tired of scanners that miss everything. The professional serverside services (serversiding.xyz, serverside.fun, aureus.wtf) all use heavily obfuscated backdoors hidden inside models. DarkX is my attempt to build something that can actually find those. It’s not perfect – no scanner is – but after a lot of trial and error it’s become reliable enough to catch even the sneaky ones. How to get started You’ll need a key – they expire every two days (keeps things fresh). Drop your key in the box, hit Validate, and the tool loads up.

it always dosent run a backdoor like: (ran 0/7 backdoors)
add disconnecting players
what games does it work in and have u tested it in?
im using solara v3 , maybe try using a serverside for this
Bro pls fix ur key system I hate work ink omg bro
what executors does It work well with?
can u make a backdoor script that work with this executor? i tried many backdoors but none worked